AI Risk Management for the AI You Already Use
AI now reaches your organization through vendor updates, employee tools, and agents that act on your systems. STIG helps you find it, assess the risk it introduces, put proportionate governance in place, and test that your controls hold, so you can adopt AI with confidence.
Frameworks We Align To
We apply these alongside the regulatory and contractual obligations your organization already carries.
Who We Serve
- Organizations rolling out AI assistants and copilots to their workforce
- Teams building AI applications, agents, or integrations on their own data
- Regulated organizations whose vendors are adding AI to existing platforms
- Executives and boards who need a defensible position on AI risk
We bring this work to every industry we serve, including healthcare, financial services, and critical infrastructure.
Top Risks We See in AI
- AI features enabled by vendor updates that never went through review
- Sensitive data entered into AI tools the organization never approved
- Agents and integrations holding broader credentials than their task requires
- Prompt injection that turns documents, emails, or web content into instructions
- AI assistants surfacing information through overly broad existing permissions
- No monitoring once an AI tool is in production
What We Deliver
How We Work Safely
- We minimize disruption to clinical workflows
- We don't access live patient records unless explicitly authorized
- We align security improvements to patient-care continuity
- We assess, test, and govern AI; we don't certify AI systems or declare them compliant
Your AI Risk Journey
From the first inventory to ongoing oversight, we stay with you through the full AI risk lifecycle.
Why Organizations Choose STIG

Ready to Get Ahead of AI Risk?
Let's discuss how STIG can help you understand the AI already in your environment and build governance that keeps pace with adoption.
Team
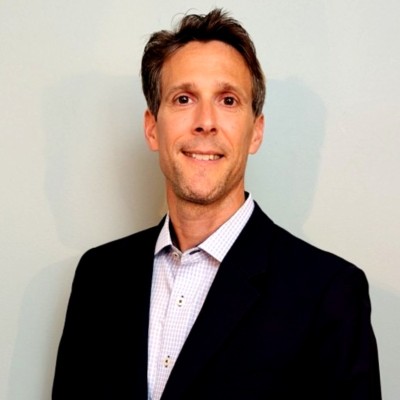
Jon (Jonathan C.) Kobrick
Founding Partner
Jon (Jonathan C.) Kobrick is a cybersecurity and IT leader with 25+ years of experience helping organizations build security programs that fit the way they operate—practical, right-sized, and aligned to real-world risk. He leads STIG's AI risk management practice, applying security governance discipline to how organizations adopt and operate AI. As a Partner and executive leader at Secure Technology Integration Group (STIG), he has spent more than two decades guiding strategy and delivery across regulated and mission-driven environments, including healthcare, financial services, insurance, and nonprofits. His work spans security program design and operations, risk assessments, incident response leadership, governance and compliance, vendor risk, and resilience planning—always grounded in clear priorities and measurable progress. Jon holds CISSP, GSEC, and GWAPT certifications, he has earned the Certified in Healthcare Privacy and Security (CHPS) credential from the American Health Information Management Association (AHIMA), and he is a member of HIMSS NYS Chapter.